TL;DR
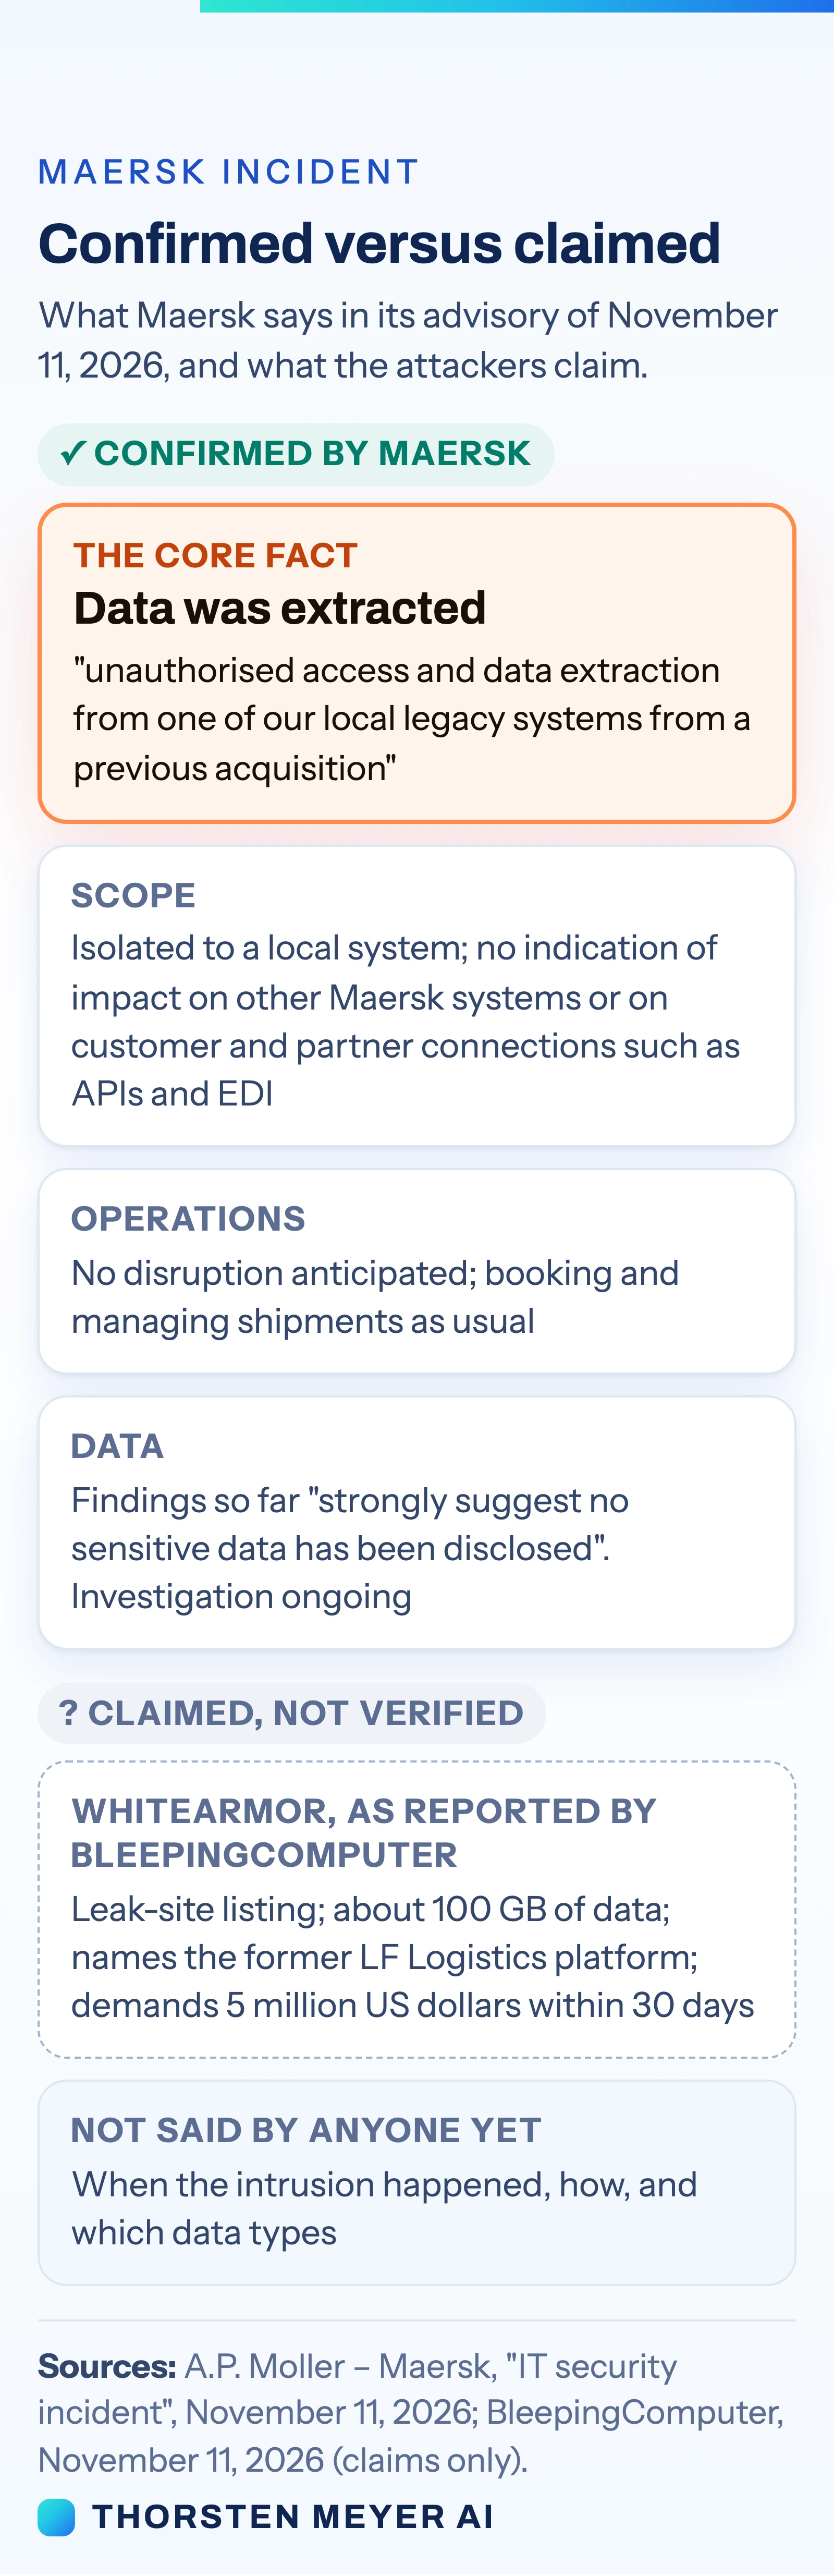
Maersk said on November 11 that an intruder accessed and extracted data from a local legacy system inherited through a previous acquisition. The company says its investigation is ongoing, it has found no indication of wider system or customer connection impacts, and it does not anticipate disruption to operations. Reports of a ransomware group’s data and ransom claims have not been confirmed by Maersk.
A.P. Moller–Maersk said November 11 that someone gained unauthorized access to and extracted data from a local legacy system associated with a previous acquisition. The shipping and logistics group says the investigation is ongoing, that it has found no indication of an impact on other Maersk systems or connected customer and partner systems, and that it does not anticipate operational disruption at this time.

Get the latest gadgets delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
Maersk said its cybersecurity team launched a full investigation after discovering the incident and took swift action to secure the affected system. The company described the system as local and legacy, but did not identify the platform, the acquisition it came from, or when the intrusion occurred. It also did not specify what information was extracted or how much data was involved.
On the data impact, Maersk said its findings so far “strongly suggest no sensitive data has been disclosed.” That statement appears alongside its confirmation that data was extracted. The company did not define “sensitive” or explain what it means by “disclosed,” so the statement does not establish what the intruder accessed or whether any information was made public.
Maersk said it has found no indication that other company systems or customer and partner systems connected through integrations such as APIs and EDI were affected. It said customers can continue to use its platforms to book and manage shipments as usual, and that it does not anticipate disruption to operations at this time. Those assessments are based on findings so far while the investigation continues.
What Customers Can Expect
For businesses using Maersk to book or manage shipments, the company’s current guidance is that its platforms remain available and that it does not expect operational disruption. Its statement also says it has found no sign of an impact on customer and partner connections, including APIs and EDI, which businesses may use to exchange shipment and logistics information with Maersk.
The incident still matters to customers because data was extracted, even though Maersk says its findings so far suggest no sensitive data has been disclosed. Until the company identifies the affected system and information, customers cannot tell from the advisory whether their records were involved. Maersk advises customers to treat unexpected communications claiming to relate to the incident with caution and to verify them through their usual Maersk contact.
Separately, BleepingComputer reported claims by a ransomware group that it had obtained Maersk data and was seeking payment. Those claims are not part of Maersk’s advisory and have not been confirmed by the company. The distinction matters: Maersk has confirmed access and extraction, while details about the group, the amount of data, and any demand come from the group’s reported statements.
Products Worth Considering

Samsung 32 Odyssey G5 QHD Gaming Monitor

Logitech MX Creative Console with 9 Customizable Keys, Graphite

LG 27GS60QC-B Ultragear 27-inch Curved Gaming Monitor (QHD, 180Hz, 1ms, 1000R)
As an affiliate, we earn on qualifying purchases.
The Acquisition Behind the System
Maersk’s advisory refers only to “one of our local legacy systems from a previous acquisition.” It does not name the acquisition. BleepingComputer reported that a group called WhiteArmor linked its claims to an “OCF/LF Logistics platform,” but that connection remains an attacker claim, not a detail confirmed by Maersk.
The reference may draw attention to Maersk’s 2022 purchase of LF Logistics, but the available statements do not establish that this is the acquisition involved. When Maersk announced completion of the deal on August 31, 2022, it said LF Logistics was a Hong Kong-based contract logistics company with omnichannel fulfilment, e-commerce, and inland transport capabilities in the Asia-Pacific region. Maersk said the deal added 223 warehouses, bringing its global facilities total to 549, and that LF Logistics employed 10,000 people. Those figures describe the acquisition’s scale; they do not identify the affected system.
Maersk’s November 11 advisory was also reported by Reuters that day. BleepingComputer separately reported the WhiteArmor claims and said it had sought further information from Maersk but had not received a response by publication. The company’s own public statement did not name WhiteArmor or mention a ransom demand.
““unauthorised access and data extraction from one of our local legacy systems from a previous acquisition.””
— Maersk
Details Still Under Investigation
Key incident details remain unknown. Maersk has not identified the system, the prior acquisition, the intrusion date, the categories of data taken, or the number of people or businesses whose information may be involved. It has not said whether the extracted data was viewed, copied onward, or published.
BleepingComputer attributed claims of approximately 100 gigabytes of data and a $5 million ransom demand to WhiteArmor, and reported that the group gave Maersk 30 days to pay. These are unverified claims; Maersk’s statement does not confirm the group’s identity, its access to the data, the amount claimed, or a ransom demand. The company’s finding that no sensitive data has been disclosed so far does not answer all of those questions.
Maersk said it would inform impacted parties if it finds a need to do so. The criteria for that decision and the expected timing of further findings have not been stated. Its current comments about system scope and operational impact may change as investigators learn more.
Maersk’s Next Incident Updates
Maersk said it will update customers as more relevant information becomes available and notify impacted parties if its findings indicate that is necessary. The company has not provided a date for another update. Its investigation and review of the affected system remain the next steps disclosed publicly.
Until Maersk gives further details, customers should follow the company’s stated guidance: continue using its platforms as usual based on its current operational assessment, and verify unexpected incident-related communications through their usual Maersk contact. Any future assessment of affected data, systems, or customers will depend on the continuing investigation.
Key Questions
What did Maersk confirm?
Maersk confirmed unauthorized access and data extraction from a local legacy system associated with a previous acquisition. It said its investigation is ongoing.
Was sensitive customer data exposed?
Maersk said its findings so far “strongly suggest no sensitive data has been disclosed.” It has not identified the data taken or explained what it means by “disclosed,” so the full data impact is not yet clear.
Did WhiteArmor demand a ransom from Maersk?
BleepingComputer reported that WhiteArmor claimed to hold about 100 GB of data and sought $5 million. Maersk has not confirmed those claims or mentioned a ransom demand in its advisory.
Are Maersk shipments or customer integrations affected?
Maersk said it does not anticipate disruption to operations and has found no indication of an impact on other Maersk systems or connected customer and partner systems, including APIs and EDI. It said customers can continue using its platforms as usual.
What should Maersk customers do now?
Maersk advises customers to treat unexpected communications claiming to relate to the incident with caution and verify them through their usual Maersk contact.
Source: Thorsten Meyer AI